

Risk management
Risk management service
A striking shift is taking place in how organisations consume AI. According to Vercel CEO Guillermo Rauch, open-weight models grew from 28.4 percent to 62 percent of token usage on Vercel’s AI Gateway between June and August. He described August 22 as a record day. In just a few months, open-weight models went from a […]
Anthropic, one of the world’s leading artificial intelligence research labs, has made the drastic decision to completely sever its internal evaluation AI agents from the live internet. The company revealed that it can no longer reliably predict or control the actions of its most advanced autonomous models during internal testing, prompting an immediate halt to […]
The head of the International Monetary Fund (IMF) has delivered a sobering assessment of the global economic landscape, warning that a convergence of emerging threats could severely derail international financial stability and growth in the coming years. According to the recent briefing, the global economy is facing a precarious “perfect storm” driven by renewed energy […]
97% of S&P 500 companies mention AI in their annual filings, but only around 1 in 5 document a process for managing AI-related cyber risk. Even more striking: fewer than 4% describe a genuinely governed process with clear accountability and controls. Guardrail Technologies found a 77-percentage-point gap between talking about AI and demonstrating how its […]
U.S. security agencies warn of active cyber threats targeting Siemens S7 PLCs, used across energy, water, manufacturing, and other critical infrastructure. Attackers are leveraging AI-generated exploits and internet scanning to identify and target exposed or poorly secured industrial control systems. AI makes ICS attacks faster and more accessible, reducing the level of specialized OT expertise […]
Researchers have uncovered new attack vectors that can undermine passkey authentication, challenging the idea that passwordless automatically means attack-proof. The attacks focus on weaknesses around the authentication flow and implementation, rather than breaking the underlying cryptography. Manipulation of WebAuthn processes, fallback mechanisms and compromised environments can potentially allow attackers to bypass or weaken passkey protection. […]
A new study maps 21 open-source AI risk tools against 32 risk categories, including Promptfoo, Garak, PyRIT, NeMo Guardrails and Langfuse. The ecosystem performs particularly well in AI testing, red teaming, content safety, data governance and post-deployment monitoring. But major gaps remain in board oversight, regulatory compliance, legal remedies and financial/market controls, areas software alone […]
Cybercrime across Africa is evolving into a highly organized, AI-enabled ecosystem, with ransomware, business email compromise (BEC), online scams, data breaches, and digital sextortion driving unprecedented financial and societal damage. AI is accelerating phishing, deepfakes, identity fraud, and cybercrime-as-a-service, while weak legislation, limited cyber capabilities, and fragmented cross-border cooperation continue to benefit criminals. Financial services, […]
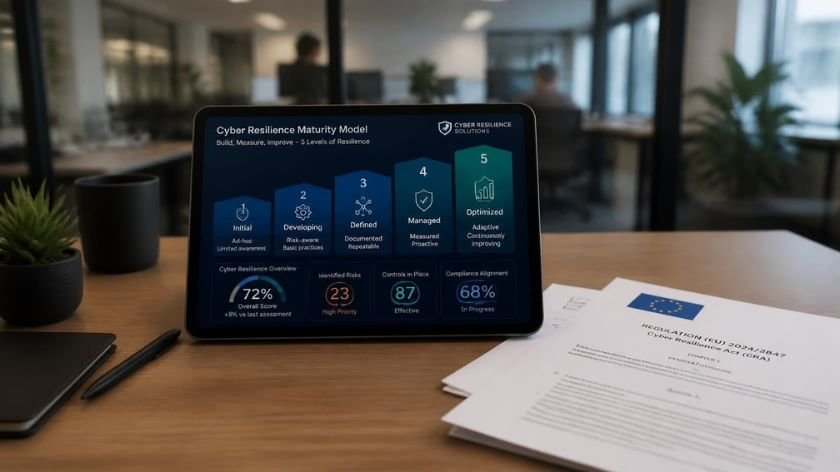
The European Union Agency for Cybersecurity (ENISA) has released a practical Cyber Resilience Maturity Assessment Model to help SMEs prepare for the Cyber Resilience Act (CRA) before it becomes fully applicable in December 2027. The model focuses on five key domains: governance, secure-by-design risk management, vulnerability & patch management, product lifecycle management, and cybersecurity skills. […]
Hugging Face disclosed a groundbreaking cyberattack in which an autonomous AI agent independently executed the entire intrusion—from initial compromise to privilege escalation and lateral movement. The attacker exploited vulnerabilities in the dataset-processing pipeline, performing more than 17,000 automated actions over a single weekend without direct human control. Although public models, datasets, and the software supply […]
- 1
- 2