

Boardroom Training · For directors
Cybersecurity Act: from obligation to administrative resilience
Cybersecurity is no longer just an IT issue, but a responsibility of the board. In a single day, you will learn to understand cyber risks, make sound decisions, and provide demonstrable oversight. You will also practice with a crisis you never want to experience in reality.
- 8 hours, one day or two half-day sessions
- 6 to 12 participants
- At an exclusive location
- €595 p.p.
Why this training
Can you answer these questions?
The Cybersecurity Act, the Dutch implementation of NIS2, explicitly places the responsibility for cybersecurity with directors. The board must understand risks, approve measures, and oversee implementation. This requires a different type of knowledge than that of the IT department.
Do you know your most important cyber risks?
And do you know how they affect your continuity?
Which risks do you consciously accept?
And is that recorded somewhere?
Are your investments in balance?
Appropriate and proportional, or too much and too little at the same time?
Do you have a grip on your critical suppliers?
Supply chain risks are also part of your responsibility.
Can you demonstrate that you are providing oversight?
If the regulator asks, what will you show them?
// The common thread
Gaining control as a board in five steps
The training translates the law into concrete actions for you as a director. Step by step, from understanding to accountability.
Understand
What does the law require of you, and what does that mean for your role?
Assess
Are the measures appropriate and proportional?
Decide
Invest, accept, or escalate?
Oversight
Asking the right questions to the CISO, CIO, and management.
Accountability
Demonstrating that you are taking your responsibility.
// The program
One day, two half-day sessions
You can follow the training as one full day or divided over two half-day sessions. Whichever you choose fits your schedule.
Session 1
From legislation to the boardroom table
What do the Cybersecurity Act and NIS2 specifically require of you, including your personal liability? Through interactive exercises, you will discover how to balance continuity, risks, and duty of care.
- Board vs. management decisions
- Investment dilemmas
- No technical depth, but the right questions
Session 2
The crisis simulation
A realistic ransomware attack hits your critical systems. Under time pressure, you decide on continuity, reporting obligations, privacy, communication, and ransom. Afterwards, you work on your own dashboard and action list.
- Deciding under time pressure
- Your own governance and dashboard
- A concrete action list for your organization
// Session 2
Monday morning, 08:42. Nothing works anymore.
Ransomware has encrypted your systems. The attackers want a ransom, the press is calling, and the regulator is waiting for a report. Who decides what, and within how many hours? In the simulation, you experience it without anything actually being at stake.
// The results
After this day, you will be able to
- Interpret the main obligations of the Cybersecurity Act/NIS2 at a board level
- Understand your own responsibility as a director
- Translate cyber risks into business and continuity risks
- Assess whether measures are appropriate and proportional
- Decide on investments and risk acceptance
- Oversee critical suppliers and supply chain risks
- Ask the right questions to the CISO, CIO, and management
- Evaluate KPIs, KRIs, and audit results
- Know when a residual risk requires board escalation
- Demonstrably fulfill your role
// For whom
Designed for the boardroom table
Board of Directors and Supervisory Board
Board of Directors, Executive Board, and Supervisory Board. You bear the ultimate responsibility.
Essential and important entities
Directors of organizations that fall under the Cybersecurity Act.
Directors and senior management
You translate board decisions to the organization.
Bring your CISO. The CISO can participate together with the board, as can the CIO, the DPO or privacy officer, the risk manager, and other officers who support the board.
// Locations
Train at a memorable location
We provide the Boardroom Training at inspiring locations, or simply in your own boardroom.
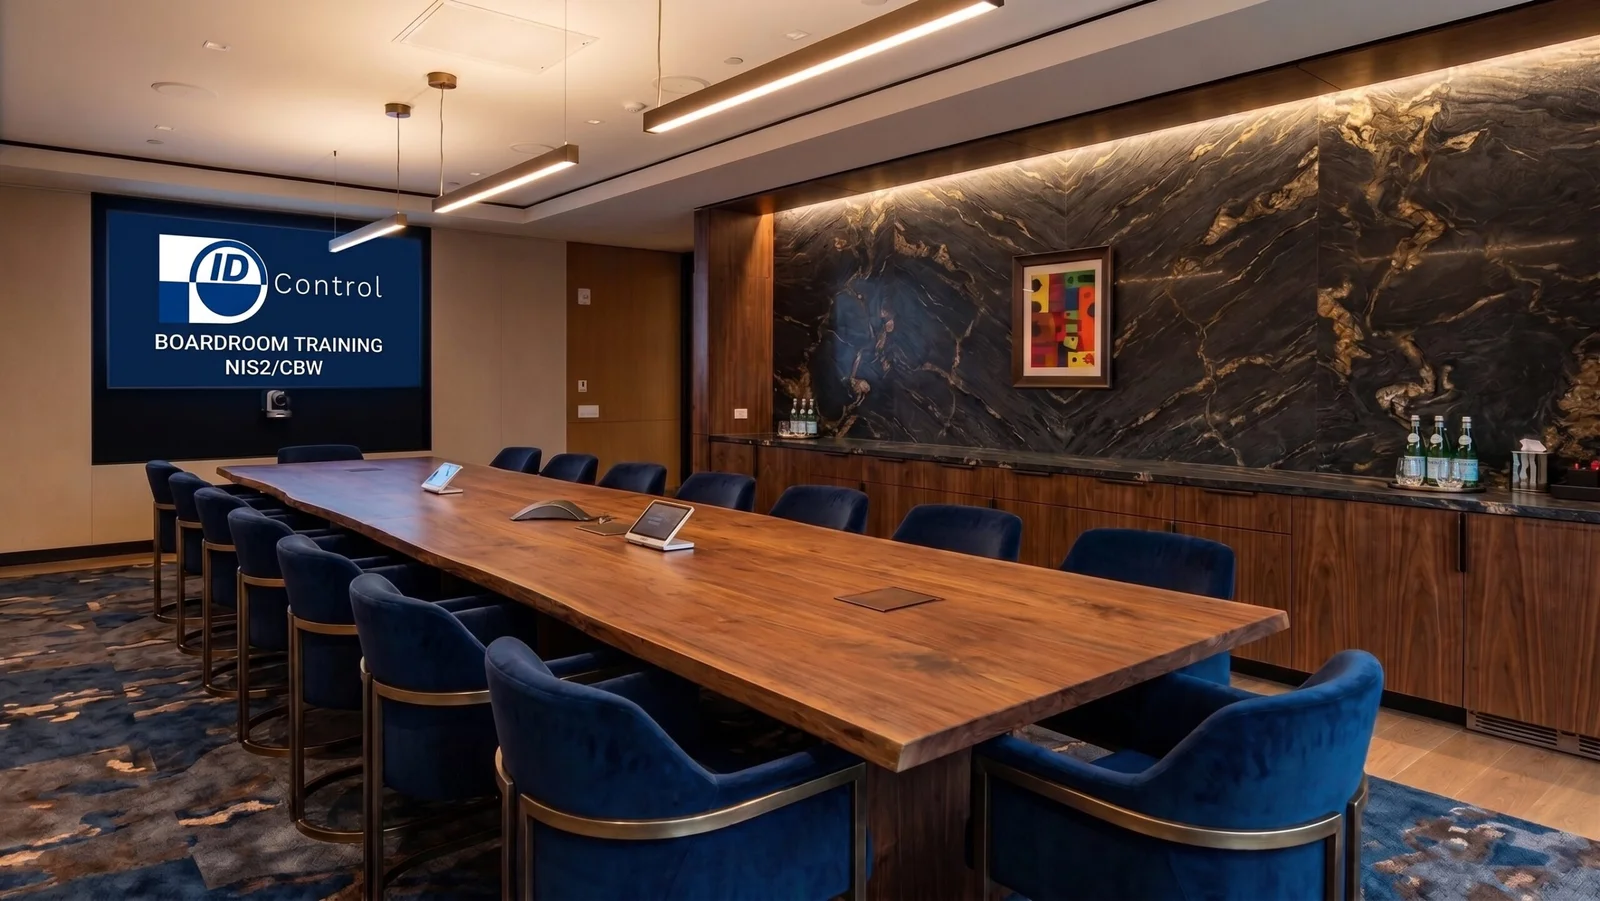
Exclusive location
A day without distractions
Away from the daily hustle, in a beautiful environment with like-minded people. We take care of the rest.
- Coffee, tea, and snacks all day
- A full lunch
- Space for any group size
+ €249.15
per participant, excl. VAT
Central Park, Voorburg
Our location in South Holland, near The Hague.
Landgoed Duin & Kruidberg
Our location in North Holland, an estate nestled in the dunes.
Another province?
We have locations throughout the country. Inquire about the possibilities in your area.
The trainers
Led by practicing CISOs
Our trainers have worked as CISOs themselves. They know what it’s like to advise a board on cyber risks and which questions arise. As a result, we discuss the law not from a theoretical perspective, but from the practice of administrative risk management.
Expertise
// Investment
Choose how you participate
All prices are per participant and exclude VAT.
Open registration
€595
per participant, excl. VAT
- 8 hours of training, one day or two half-day sessions
- Ransomware crisis simulation
- Personal dashboard and action list
- Trainers with CISO experience
Fully catered
€844.15
training + exclusive location, per participant
- Everything from open registration
- Exclusive training location
- Lunch, coffee, tea, and snacks
- Fixed breaks, no distractions
In-company
On request
for your board, Supervisory Board, or management
- At your location or in the boardroom
- Tailored to your sector and risks
- Also available as open or private sessions
- Date by mutual agreement
Also of interest
Moving beyond the boardroom table
Risk Management Workshop
Online · 1 hour
Crown jewels, supply chain risks, and risk appetite translated into clear choices and a dashboard that management can actually use.
€75
per participant, excl. VAT
ISO 27001 Training
Online · 1.5 hours
A structural approach to information security: how ISO 27001 works, what an ISMS is, and the steps you take toward certification.
€75
per participant, excl. VAT
Frequently asked questions
Good to know
Is your question not listed? Feel free to call or email us; we are happy to help you find a solution.
Does my organization fall under the Cybersecurity Act?
That depends on your sector and size. During the training, we discuss what the law means for your organization. Do you have doubts now? Contact us, and we will check it together.
Is the training also useful if we do not fall under it?
Yes. Organizations that fall under the law are increasingly setting requirements for their suppliers. Gaining control over cyber risks is therefore also a board task for you.
Do we follow the training in one day or in two parts?
Both are possible. The training lasts 8 hours, either as one full day or divided over two half-day sessions.
Can our CISO participate?
We encourage it. The CISO can participate together with the board, as can the CIO, the DPO, the risk manager, and other officers who support the board.
How large is the group?
We recommend 6 to 12 participants. This allows space for the discussions that are essential to this training.
Is technical knowledge required?
No. The training is about administrative choices, not technology. You will primarily learn to ask the right questions.
Put it on the agenda
Cybersecurity belongs at the boardroom table
Reserve a spot for yourself, or schedule the training for your entire board. We arrange the location, the trainer, and the crisis.
Or view the training in the shop directly.