Assess not only yourself, but also your processors and suppliers on their information security. Perform an audit on a third party, link the relevant contact person, and test against the framework that suits that party.
Choose the processor, supplier, or other third party you wish to assess.
2
Link contact person
Add the contact person involved in the audit on behalf of the third party.
3
Choose framework
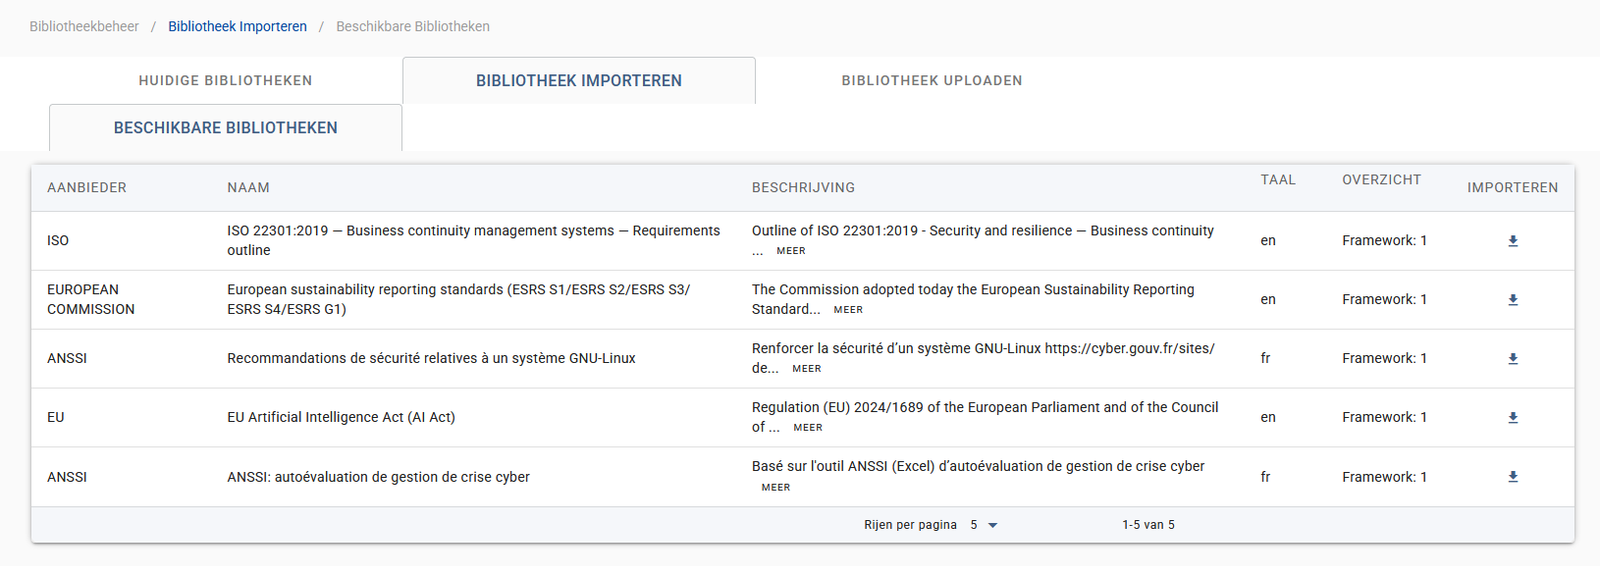
Select the compliance framework you are testing against from a large library of frameworks.
4
Perform audit
Assess the third party point by point against the chosen framework.
A large and growing range of frameworks
You are not limited to a single fixed standard. Choose from a large library of frameworks, appropriate for the sector and risk profile of the third party you are assessing.
Linked to other features
The third party itself
The party you audit is the same entity you record in Third-Party Management.