






The court has officially ruled that the notorious Citrix hack at the Public Prosecution Service (OM) was a situation of force majeure. This decision is based on the fact that it involved an unknown zero-day vulnerability that lay entirely outside the organization’s influence and sphere of risk. A crucial element in this ruling was that […]
The municipality of Enschede has published an explanation regarding the policy on the deployment of cameras with facial recognition technology in public spaces. The use of this type of advanced biometric technology inevitably raises critical questions about the protection of citizens’ privacy. Under the strict rules of the General Data Protection Regulation (GDPR), the processing […]
The European Union is preparing to present a new and stringent legislative proposal this coming Thursday aimed at the protection of minors. These new rules are intended to protect children much more effectively against online risks, such as addictive algorithms, harmful content, and privacy violations. The proposal likely builds on existing frameworks such as the […]

The European Commission has confirmed that cybersecurity agency ENISA will be granted direct access to powerful models such as Anthropic’s Mythos 5 and OpenAI. The purpose of this access is to independently investigate the capabilities and potential impact of these advanced technologies on cybersecurity. This step marks a significant shift in European AI governance: moving […]
On September 10, the House of Representatives will discuss the future of the European Business Wallet (EBW) and eIDAS with both public and private parties. The message is clear: ensure speed, interoperability, and a strong public-private ecosystem in which the government and the market collaborate. Digital wallets make data minimization and purpose limitation practical: only […]
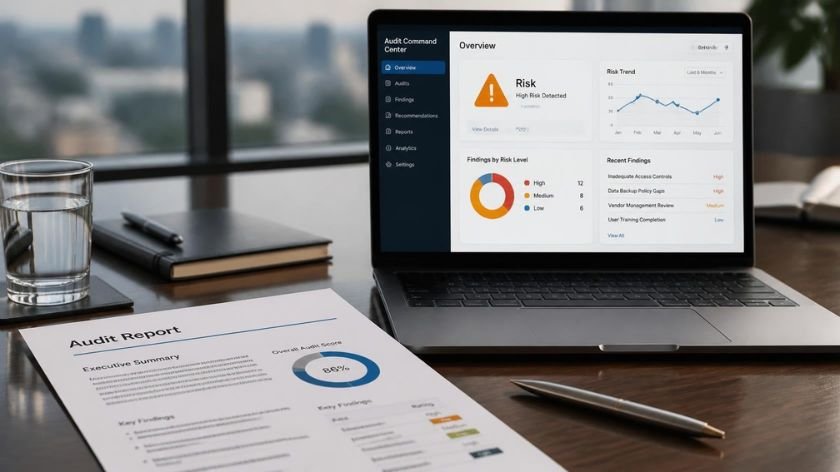
The central government is increasingly using the public cloud, but governance, risk management, and strategic direction are not keeping pace. Of the 126 material public cloud services, no prior risk assessment was conducted for as many as 67% regarding sovereignty, continuity, and data protection, among other factors. Furthermore, the dependence on primarily American hyperscalers creates […]
State Secretary Aerdts believes the online world is currently insufficiently safe for children and is therefore calling for a European minimum age for social media. According to her, social media platforms must take more responsibility for protecting minors against harmful content and addictive algorithms. Simultaneously, the government is launching a campaign to encourage parents to […]

The Cybersecurity Act implements NIS2, but according to the author, it aligns too closely with existing sectoral structures instead of achieving true harmonisation. Especially now that digital threats, ransomware, and supply chain risks are increasing, collective European cyber resilience is essential. NIS2 should not be adapted to the Dutch status quo; instead, organisations and regulations […]
80% of European companies believe they have control over their email, while approximately half are dependent on non-European providers. 56% fear that corporate data could become accessible through extraterritorial legislation such as the US CLOUD Act. Data storage in Europe does not automatically mean data sovereignty: the jurisdiction under which the provider falls is also […]
The EDPS is deeply concerned about the European Commission’s plans to significantly expand Europol’s powers. Europol would soon be permitted to process personal data for long periods from individuals with no demonstrable links to crime. The watchdog warns of the increased volume of data, new data categories, and insufficient oversight and safeguards. The EDPS demands, […]