






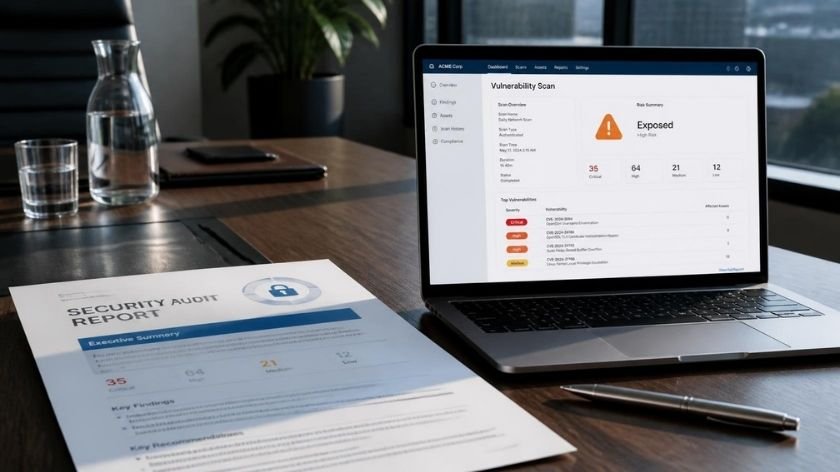
Many cyberattacks are not sophisticated, but instead exploit known and often easily preventable security issues. CISA primarily observes the exploitation of vulnerabilities such as SQL Injection, command injection, missing authentication, and poor input validation. Publicly accessible services such as RDP, SMB, and Telnet also frequently provide an easy entry point for attackers. Organizations must patch […]
CISA updated the Zero Trust Maturity Model (ZTMM) which provides a roadmap for agencies to reference as they transition towards a zero-trust architecture. ZTMM also provides a gradient of implementation across five distinct pillars to facilitate federal implementation, allowing agencies to make minor advancements toward optimization over time.CISA encourages state, local, tribal, and territorial governments, and […]
Microsoft’s market dominance creates a big disucssion as they also have the most critical vulnerabilities. Does your organisation assess the 3rd party risk of technology suppliers?
Using only a password to access or manage systems remotely is unwise and should be seen as a “bad practice,” according to the Cybersecurity and Infrastructure Security Agency (CISA) of the US Department of Homeland Security. In June, the CISA decided to collect bad practices that are extremely risky and actually increase cyber risks for […]